By FindAttorneys.org Editorial Team | Legal Technology & Practice Management | Last reviewed: October 2026
Quick answer: Good legal redaction software should permanently remove sensitive information from the final file, not merely cover it visually. Law firms should test how a tool handles text layers, OCR, metadata, comments, embedded objects, repeated identifiers, and exported PDFs. The right product also depends on document volume, workflow, staff training, access controls, and the filing rules that apply in the relevant court.
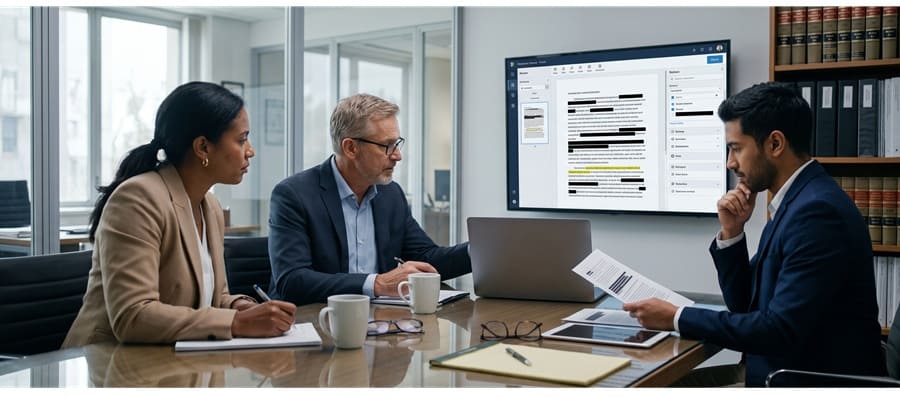
Redaction looks simple until a document contains more than what appears on the screen. A Social Security number can be hidden under a black rectangle while remaining searchable or copyable. A scanned record can carry an OCR text layer. A Word or PDF file may retain comments, revision history, embedded objects, or metadata that reveals information the reviewer thought was gone.
For law firms, that makes redaction more than a formatting task. It is part of confidentiality, filing compliance, discovery practice, and information governance. Software can reduce repetitive work, but it does not replace legal judgment about what must be redacted, what should remain visible, or whether a document should instead be filed under seal.
Start With the Legal Requirement, Not the Software Feature List
Federal Rule of Civil Procedure 5.2 requires parties filing in federal civil cases to limit certain personal identifiers in public filings. Subject to exceptions and court orders, the rule generally permits only the last four digits of Social Security and taxpayer-identification numbers, the year of birth, a minor’s initials, and the last four digits of a financial-account number. The rule also makes clear that responsibility for redaction rests with the filer, not the clerk. Federal Rule of Civil Procedure 5.2
Other courts have their own local rules, standing orders, electronic-filing procedures, and privacy requirements. Criminal, bankruptcy, appellate, family, juvenile, and state-court matters may use different standards. A firm therefore should not buy software based on a generic claim that it is “compliant.” The software must support the firm’s actual filing obligations, while the lawyers and staff still decide what the law requires in each matter.
The federal courts also warn that the filer is responsible for removing protected personal information before a document enters CM/ECF. U.S. Courts CM/ECF privacy guidance notes that Civil Rule 5.2, Criminal Rule 49.1, Bankruptcy Rule 9037, and Appellate Rule 25(a)(5) impose redaction requirements for particular personal identifiers.
Why Visual Redaction Is Not Enough
A black box is not a redaction if the underlying data survives. Federal court guidance has specifically warned against methods such as changing text to white or placing a black rectangle over text when the concealed content can remain recoverable. The same guidance cautions that word-processing files may contain hidden metadata, revision history, notes, and other information. U.S. District Court guidance on redaction best practices
A proper redaction workflow should therefore be designed around removal and verification. The final question is not “Can I see the sensitive text?” It is “Can the sensitive information still be recovered from the file?”
The Main Categories of Legal Redaction Tools
The original draft correctly identified that firms tend to encounter several broad categories of tools. The categories are useful, but they should be evaluated by risk and workflow rather than by marketing labels.
Manual markup or improvised masking: Drawing shapes over text or changing font colour can create the appearance of redaction without deleting the underlying information. This is the highest-risk approach when the final document remains electronically searchable or contains accessible layers.
Built-in redaction functions in general PDF software: These tools may be sufficient for firms handling modest volumes if they truly apply redactions, sanitize hidden content, and support verification. The key is whether staff understand the difference between annotation tools and actual redaction functions.
Dedicated redaction platforms: Specialized products may add batch processing, search-and-redact, pattern recognition, OCR, role-based permissions, logs, review queues, and quality-control features. These capabilities can matter when a firm processes large discovery sets or repeat categories of protected information.
Review-platform or e-discovery redaction: Litigation teams may redact inside broader document-review platforms. The advantage is that redaction can be integrated with coding, privilege review, productions, and audit history, but firms still need to test what happens when documents are exported or converted for filing.
Eight Questions to Ask Before Choosing Redaction Software
- Does the tool permanently remove the selected text or image data from the final file?
- How does it handle OCR text layers in scanned PDFs?
- Can it detect and remove metadata, comments, annotations, hidden layers, attachments, and document properties?
- Can reviewers search for repeated identifiers such as names, account numbers, dates of birth, or medical-record numbers across a document set?
- Does it support a second-review or approval step before files are produced or filed?
- Does it create a useful audit trail showing who applied or approved redactions and when?
- What access controls, encryption, retention settings, and data-hosting arrangements apply to files processed through the product?
- Can the firm export a final PDF and independently verify that the redacted information is no longer recoverable?
Use Product Comparisons as a Starting Point, Not as Proof of Compliance
Firms researching the market may find it useful to review a third-party category comparison of legal redaction tools for law firms. A comparison can help identify products or features worth testing, but it should not substitute for independent due diligence. Security claims, “compliance” labels, pricing, hosting arrangements, OCR accuracy, and audit features should be verified directly with the vendor and tested against the firm’s own workflow before purchase.
That distinction is important because no software product can determine every legal obligation for the firm. A tool may correctly remove selected text while the reviewer selects the wrong information, overlooks a local rule, or files a document that should have been sealed instead of publicly redacted.
Confidentiality Duties Should Shape the Evaluation
ABA Model Rule 1.6(c) states that a lawyer must make reasonable efforts to prevent inadvertent or unauthorized disclosure of, or unauthorized access to, information relating to the representation of a client. The ABA’s comments explain that reasonableness can depend on the sensitivity of the information, likelihood of disclosure, cost and difficulty of additional safeguards, and the effect those safeguards have on representation. ABA Model Rule 1.6 and Comment 18
The Model Rules are not themselves the governing ethics rules in every jurisdiction. Firms should check the rules adopted by the state or other licensing authority that governs the lawyers involved. Still, the confidentiality principle is useful when evaluating whether a workflow is reasonably designed to protect client information.
Build Redaction Into the Workflow, Not the Last Five Minutes
The best software can still fail when the process around it is weak. A practical firm workflow should separate the legal decision about what must be removed from the technical task of applying and verifying the redaction.
- Identify the governing filing, discovery, confidentiality, protective-order, and privacy requirements before redaction begins.
- Work from a controlled copy of the source document and preserve the original securely.
- Apply redactions using a function designed to remove information, not a drawing or highlighting tool.
- Sanitize or remove hidden information when appropriate, including metadata, comments, and embedded content.
- Export the final version using the same process that will be used for filing or production.
- Have a second reviewer check both the visible redactions and the file itself.
- Test whether redacted text can be searched, selected, copied, extracted, or revealed through metadata or document properties.
- Record the review step before the document leaves the firm.
How to Test Whether a Redaction Actually Worked
A firm should test the finished output, not just the working file. The exact steps depend on the document and software, but useful quality-control checks can include:
- Search the final PDF for the redacted word, number, or phrase.
- Try to select, copy, and paste text from the redacted area.
- Review document properties, comments, attachments, layers, and metadata that remain in the output.
- For scanned documents, check whether an OCR text layer still contains the sensitive information.
- Open the file in a second PDF viewer to confirm that the result is not dependent on one application.
- Where appropriate, use a controlled test document containing known dummy identifiers to verify the workflow after major software updates.
This kind of testing is more meaningful than a vendor demonstration using a clean sample file. The firm should know how the tool behaves with the messy documents it actually receives: scans, image-only PDFs, mixed page sizes, handwritten notes, attachments, prior annotations, and files converted from word processors.
Where the NIST Privacy Framework Fits
The NIST Privacy Framework is a voluntary risk-management framework, not a court-filing rule or legal-redaction standard. NIST describes it as a tool for helping organizations identify and manage privacy risk. That makes it useful for broader governance questions—such as roles, accountability, data handling, vendor risk, and continuous improvement—but it does not tell a law firm which identifiers must be redacted from a particular pleading.
For a firm choosing redaction technology, the framework is most useful at the policy level: who owns the process, how risk is assessed, which controls are required, and how failures are detected and addressed.
Connect Redaction to the Firm’s Broader Technology Program
Redaction should not live in isolation from other technology decisions. A firm that is improving document workflows may also want to review What Can Your Law Firm Do to Be More Efficient?, particularly the sections on legal technology, cybersecurity, and staff training.
Firms adopting AI-assisted document tools should also think about how files are uploaded, processed, retained, and reviewed. See Future-Proofing Your Law Firm: Adopting AI Without Losing the Human Touch for a broader discussion of legal-technology adoption and data privacy.
What Should a Firm Do If a Redaction Fails?
If sensitive information is discovered after a document has been sent or filed, the next steps depend on the forum, the type of information, and who received it. Delay can make the problem harder to contain.
- Stop further distribution of the affected file where possible and preserve a copy for internal review.
- Identify exactly what information was exposed, to whom, and for how long.
- If the document was filed with a court, review the applicable rules and contact the clerk or follow the court’s procedure for restricting, correcting, replacing, or sealing the filing.
- Evaluate whether the client, insurer, privacy officer, opposing counsel, regulator, or another party must be notified under applicable law, ethics rules, court orders, or contractual obligations.
- Document the cause of the failure and correct the workflow, training, or software configuration that allowed it to happen.
A failed redaction is not automatically an ethics violation, malpractice claim, or sanctionable event. Consequences depend on the facts, applicable duties, harm, and the reasonableness of the firm’s safeguards and response. That is why the article should avoid treating every technical mistake as producing the same legal result.
Match the Tool to the Firm’s Actual Work
A solo lawyer filing a few redacted exhibits each month does not necessarily need the same system as a litigation group producing hundreds of thousands of pages. The better buying question is not “Which product has the most features?” but “Which controls address the risks in our actual document flow?”
- Low-volume practice: prioritize reliable permanent redaction, sanitization, ease of use, and a simple verification workflow.
- High-volume litigation: consider batch redaction, search patterns, review queues, audit trails, privilege workflows, and integration with document-review systems.
- Medical or financial matters: pay particular attention to OCR accuracy, repetitive identifiers, access control, and handling of regulated or highly sensitive data.
- Multi-office firms: evaluate permissions, standardized settings, central administration, training, and the ability to enforce a consistent review process.
Frequently Asked Questions
Is putting a black box over text a valid redaction?
Not by itself. If the underlying text remains searchable, selectable, extractable, or recoverable from the file, the information has not been securely removed. Use a redaction function designed to delete the underlying content and verify the final output.
Does Rule 5.2 apply to every legal document?
No. Federal Rule of Civil Procedure 5.2 governs specified federal civil court filings and includes exceptions. Other courts and matter types may use different privacy and redaction rules. Firms should check the rules that apply to the particular filing.
Does legal redaction software make a filing compliant automatically?
No. Software can help remove selected information, but lawyers and staff still must identify the correct material, follow the governing rule or order, and verify the final file before filing or production.
Should a law firm remove metadata from every file?
Not automatically. Metadata can contain sensitive information, but whether it should be removed depends on the document, production protocol, filing requirements, and legal obligations. Firms should have a defined policy rather than applying one blanket rule to every matter.
Is the NIST Privacy Framework a legal redaction standard?
No. NIST describes the Privacy Framework as a voluntary privacy-risk-management tool. It can help firms structure governance and accountability, but it does not replace court rules, ethics obligations, protective orders, or jurisdiction-specific law.
How often should a firm test its redaction workflow?
Testing should occur when the workflow is implemented and after material software, configuration, or export-process changes. Firms handling sensitive documents regularly may also benefit from periodic controlled tests and quality reviews.
Disclaimer
This article provides general educational information about legal document redaction and law-firm technology. It is not legal, ethics, cybersecurity, or compliance advice. Court rules, protective orders, discovery obligations, privacy laws, professional-conduct rules, and filing procedures vary by jurisdiction and matter. References to third-party software comparisons are informational and are not endorsements. Law firms should independently evaluate products, security claims, and the requirements that apply to their own matters and clients.